CARTP Journey: Going Down the Azure Enumeration Rabbit Hole
Description
This blog talks about my CARTP certification journey which has a lot of rabbit holes and made some custom tooling along the way
Introduction
Back in December 2025, I participated in the BSides Vizag CTF and ended up winning a CARTP voucher sponsored by Altered Security.
That is where my Azure security journey started.
I had worked on different areas of security before, but Azure security introduced me to a different mindset. Instead of just looking at applications or systems, I had to understand identities, permissions, roles, and how everything connects together.
Starting CARTP
When I started the labs, my initial plan was simple: complete the objectives and prepare for the exam.
But while going through the content, I realized something interesting:
Most Azure attacks start with one question:
“What access do I actually have?”
Before exploitation comes enumeration.
- Who am I?
- What roles do I have?
- What resources can I access?
- What identities exist?
- What secrets or misconfigurations are exposed?
The deeper I went, the more I wanted to understand what was happening behind the commands.
Falling Into the Enumeration Rabbit Hole
Instead of only running existing tools, I started reading Azure documentation and experimenting.
A small script to automate a few checks slowly kept growing.
“Let me add users.”
“Let me add groups.”
“What about role assignments?”
“What about resources?”
And eventually that small script became a ~2.5K line PowerShell project.
The goal was simple:
Enumerate the hell out of Azure.
Why Build Another Tool?
There are already amazing projects in this space.
Tools like AzureHound solve a very important problem — collecting Azure data and mapping relationships for attack path analysis.
My goal was slightly different.
I wanted something:
- single file
- no external dependencies
- easy to run from PowerShell
- focused on quickly understanding an Azure environment
Things I Learned Along the Way
Building the tool forced me to understand concepts much deeper:
- Entra ID identities
- Service principals
- Managed identities
- RBAC permissions
- Azure resources
- Enumeration techniques
Sometimes building something teaches you more than only consuming material.
Exam Experience
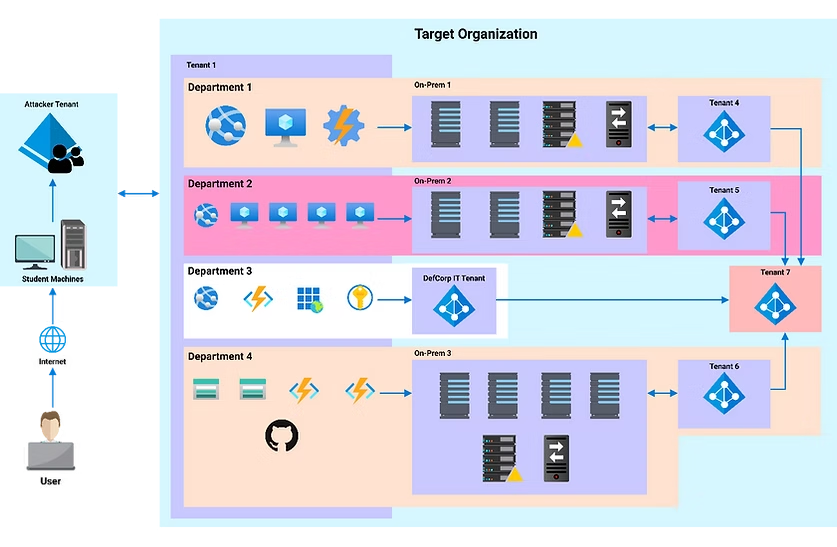
The Certified Azure Red Team Professional (CARTP) is a fully hands-on certification from Altered Security. There are no multiple-choice questions. You get a 24-hour practical exam in a live, multi-tenant Azure environment, where your goal is to compromise the resources across it.
After the exam window closes, you have 48 hours to submit a detailed report covering the attack path you took. Since the lab environment shuts down once the 24 hours are over, you need to capture screenshots and notes as you go.
The CARTP exam felt straightforward to me, largely because I had completed most of the labs beforehand and kept detailed notes throughout. The exam is mostly about enumeration: working through the environment methodically and using the clues you find to uncover and pivot to other services. If you’ve done the labs properly, the techniques will feel familiar.
I finished the technical portion in about four hours. I then spent a good amount of additional time on the report, since this was my first professional certification and I wanted to be careful. I documented each step thoroughly and included clear diagrams, so that nothing could be questioned or lead to a disqualification.
What’s Next?
I’ll be cleaning up and open-sourcing the enumeration tool soon.
CARTP started as a certification goal, but the best part was the rabbit holes it pushed me into.
Huge thanks to Altered Security and BSides Vizag for the opportunity.